

"CyberHoot has been a game-changer for us - simple to deploy, highly effective in raising awareness, and a great fit for MSPs looking to strengthen client security postures without adding complexity."
Author: Katie Boquetti | Editorial: Craig Taylor Editorial by Craig Taylor: I remember the early days of...
Read more
A malicious browser extension is a browser add-on designed to perform harmful actions or a legitimate extension...
Read more
An infostealer, short for information-stealing malware, is malicious software designed to quietly collect...
Read more
A session token is a temporary digital credential used by a website or application to remember that a user has...
Read more
Token theft is the unauthorized stealing of a digital authentication token that represents a user, device, or...
Read more
Pretexting is a social engineering technique in which an attacker creates a believable story, identity, or...
Read more
MFA fatigue, also called MFA push bombing or MFA push bombardment, is an attack in which repeated multi-factor...
Read more
Phishing-resistant multifactor authentication is authentication designed to prevent credentials from being...
Read more
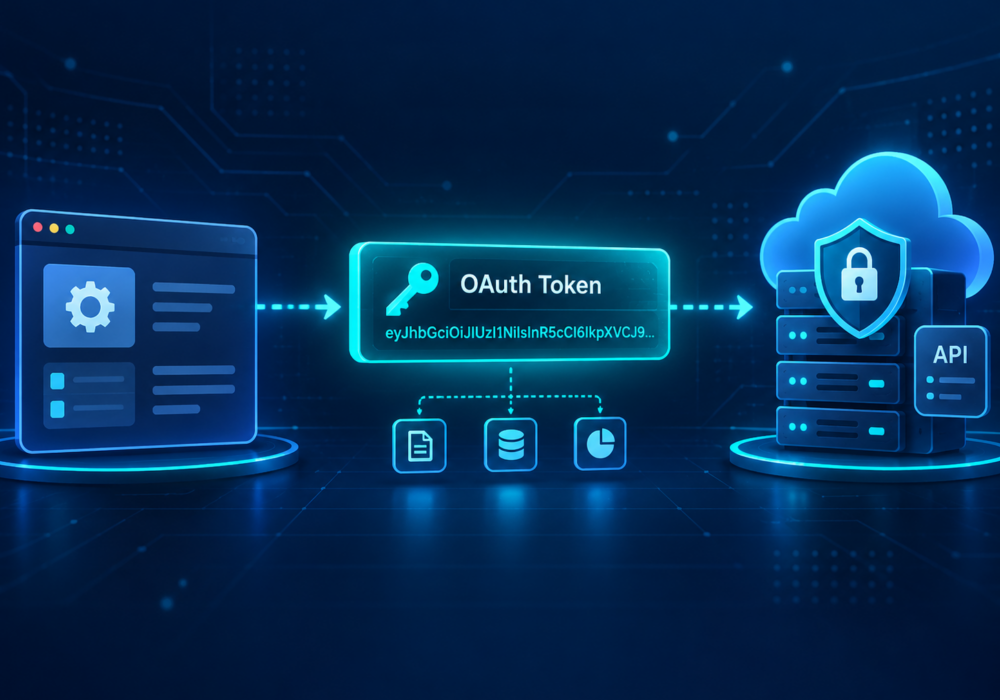
An OAuth token is a digital credential that allows an application to access specific resources on behalf of a...
Read more
This guide walks you through setting up and managing the CyberHoot–Gradient MSP integration using the...
Read moreGet sharper eyes on human risks, with the positive approach that beats traditional phish testing.
