
Blog > Page 6

Stay sharp with security insights

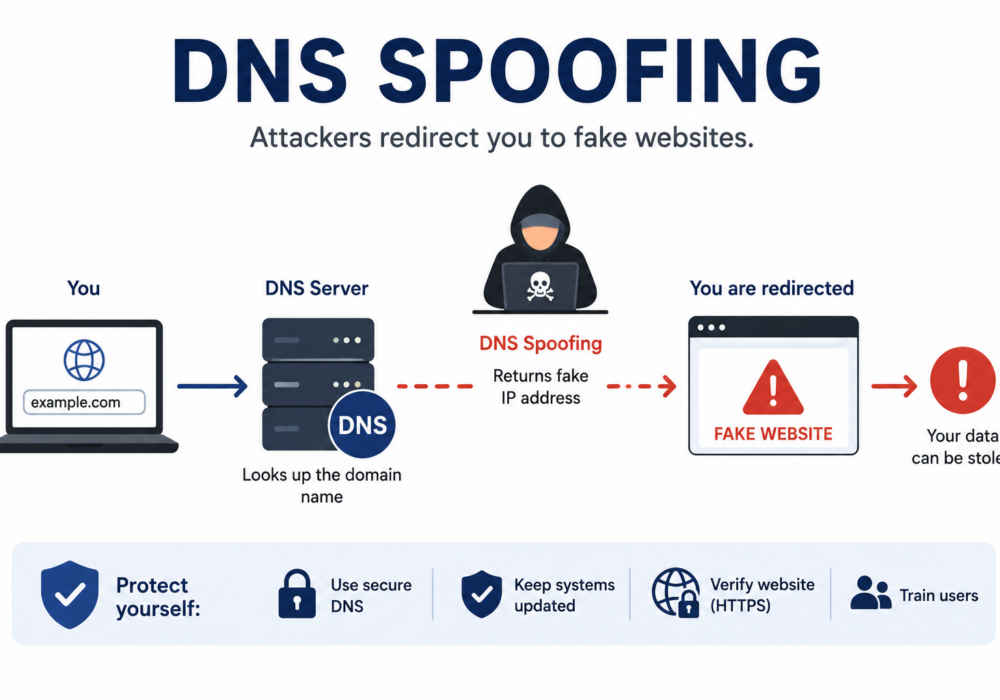
DNS Spoofing

DNS Spoofing

DNS Spoofing, also known as DNS Cache Poisoning, is a cyberattack in which an attacker manipulates the Domain...

Read more
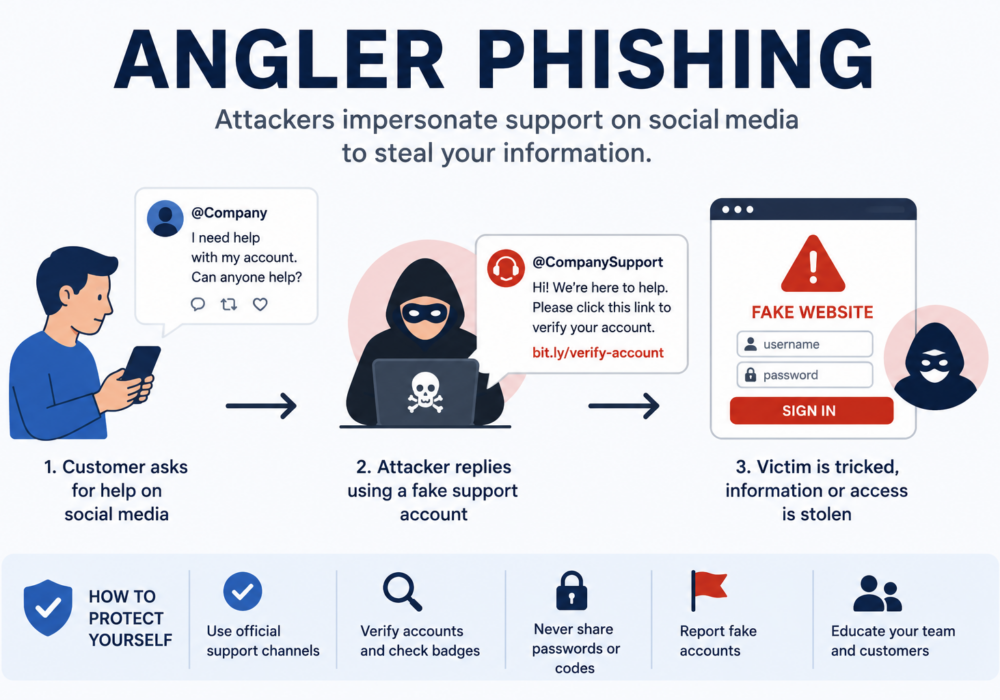
Angler Phishing

Angler Phishing

Angler phishing is a form of social engineering in which cybercriminals impersonate a company's customer support...

Read more
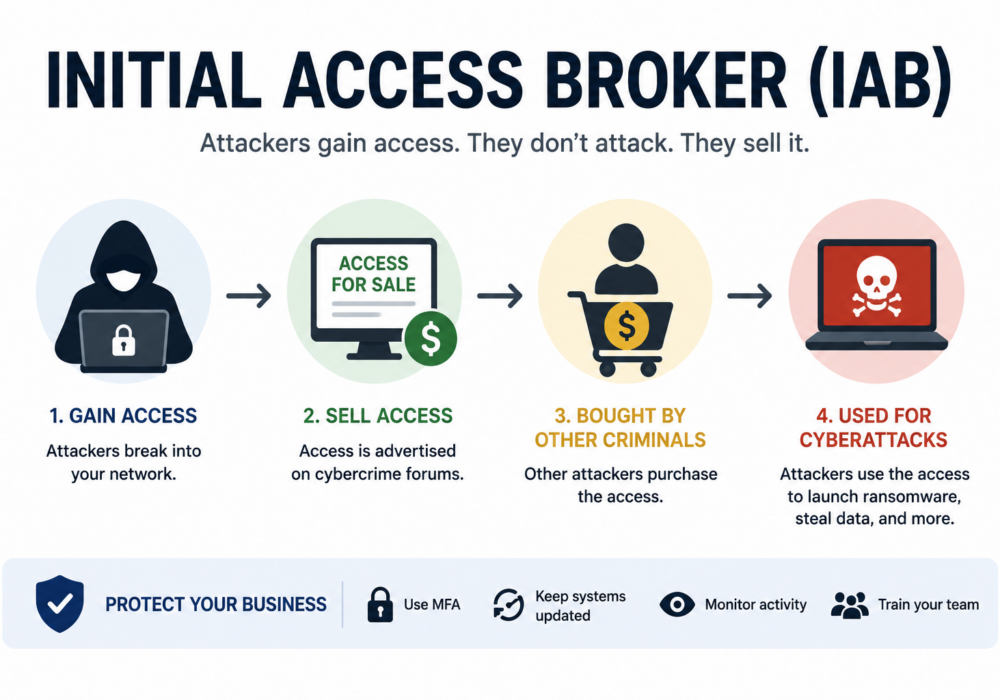
Initial Access Broker (IAB)

Initial Access Broker (IAB)

An Initial Access Broker (IAB) is a cybercriminal who specializes in breaking into organizations and then selling...

Read more

Your subscription could not be saved. Please try again.
Almost done! Check your inbox and click the link to confirm your subscription.

Passkey

Passkey

A passkey is a modern replacement for passwords. Instead of typing a password, users authenticate using something...

Read more
AI Found Your Weaknesses. Let’s Fix Them First.

AI Found Your Weaknesses. Let’s Fix Them First.

New benchmark data names MDASH and Claude Mythos Preview are the top AI agents finding zero-day vulnerabilities...

Read more
Your Identity Is Not Only a Front-Door Problem, It is an Internal Risk Too

Your Identity Is Not Only a Front-Door Problem, It is an Internal Risk Too

One Forgotten Password, Almost a Catastrophe A single Windows machine at a retail store location had a cached...

Read more
CyberHoot’s Cybersecurity Newsletter: May 2026

CyberHoot’s Cybersecurity Newsletter: May 2026

Welcome to CyberHoot's May Newsletter! Tax season has a way of consuming everything. For weeks, most business...

Read more
Why Your Clients’ Routers Are Now a National Security Conversation

Why Your Clients’ Routers Are Now a National Security Conversation

You now have five important reasons to start a router security conversation with your small business clients this...

Read more
CyberHoot’s Email-Relay IP Addresses, Domains, and Allow-list Articles

CyberHoot’s Email-Relay IP Addresses, Domains, and Allow-list Articles

Updated: May 12th, 2026 This article is a reference to CyberHoot's mail relay IP Addresses and Domain...

Read more
Your Employees Connected 47 Apps to Google Last Year. Can You Name One of Them?

Your Employees Connected 47 Apps to Google Last Year. Can You Name One of Them?

OAuth tokens don't expire when employees leave, passwords change, or apps go rogue. Your security program needs...

Read more
Attackers Don’t Need a Key. They Already Have Yours.

Attackers Don’t Need a Key. They Already Have Yours.

Most breaches don't start with a hacker in a hoodie cracking code at 3am. They start with your username and a...

Read more
CyberHoot’s Cybersecurity Newsletter: April 2026

CyberHoot’s Cybersecurity Newsletter: April 2026

This month we need to talk about something big. Not doomsday big, but pay-attention-now big. On April 7th,...

Read more
Testimonials

See who's talking about CyberHoot

“Using CyberHoot was one of the best decisions we made regarding SAT. Fully automated, training is interesting, and staff participation is high compared to other vendors.”
Michael Gibby, SEQ IT Services, Founder & Managing Director

"Single Digits chose CyberHoot to address our Awareness Training and Policy Governance needs because it was simple and effective. Unlike other LMS systems which require 45-minute training videos and dozens of trick questions, our staff receives important training in less..."
John Nelson, Single Digits, VP Engineering
"When we got phished it became pretty clear we needed to do more to protect our company. The same old training just wasn't working. CyberHoot came to the rescue. It's fun, our team loves it, and best of all, it's..."
Leo Laporte, Security Now, Host
"While it is well known that there are many cyber security threats, sorting out how to protect yourself without accidentally exposing yourself can be a daunting task. For a small organization like ours, this type expertise and time to research..."
Astrid Wielens, Zebra Crossings, Executive Director
"Using CyberHoot was one of the best decisions we made regarding SAT. Fully automated, training is interesting, staff participation is high compared to other vendors."
Max Krider, Creative Tech, HIPAA Compliance Officer