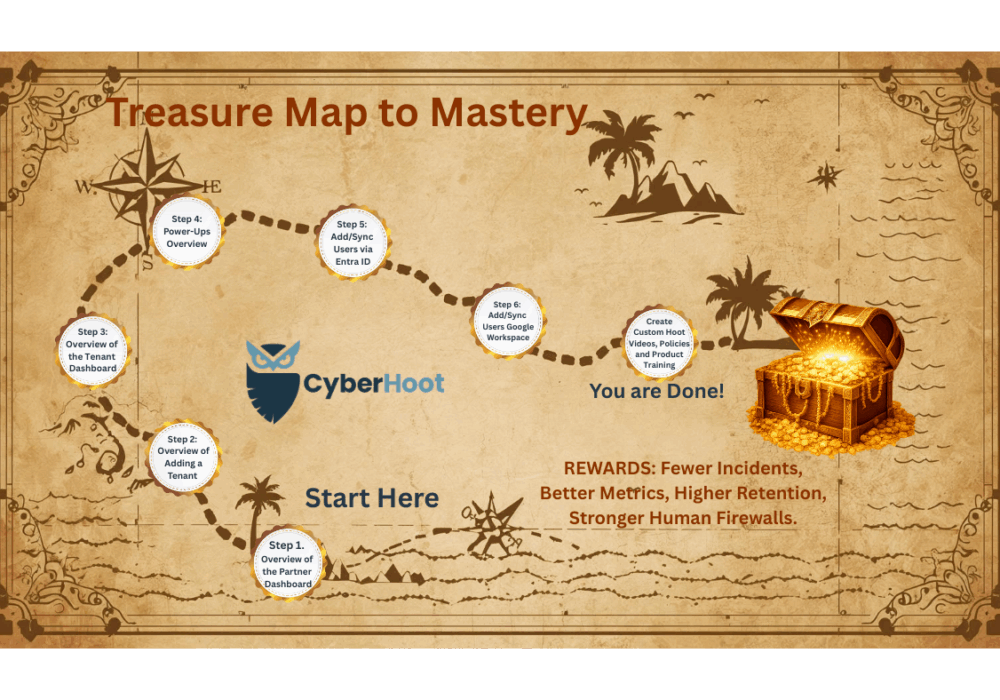
You made it! This is your visual treasure map to CyberHoot success. Below you’ll find seven quick tutorial videos covering everything from setting up tenants to creating Custom Hoots. Each tutorial is short, practical, and designed to help you scale confidently.
Bookmark this page now – it’s your go-to reference for mastering CyberHoot and scaling your success.
First Time? Watch Steps 1-3 in order (about 10 minutes)
Adding More Tenants? Jump straight to Step 2
Need a Quick Refresh? Click any step you need
There are seven (7) quick stops on this Treasure Map, each one shown above but Linked Below shows either a short video tutorial or How-To article to guide you.
Total Time: About 26 minutes to watch all tutorials
Click any Link above to watch a quick demo video. No long tutorials, no overwhelming manuals. Just quick, practical guidance when you need it.
Managing multiple groups? Each can have its own tenant with:
✅ Independent automated reporting
✅ Unique branding per organization
✅ Separate administrators
✅ Individual leaderboards
✅ Compliance competitions
✅ Comparison risk scoring
The Result? Track progress by location, department, or customer. Create friendly competition that increases engagement, compliance, and behavior change. Best of all, scale CyberHoot’s impact without adding administrative burden.
Questions? Our support team is here to help at Support@cyberhoot.com
Remember: Positive outcomes start with confident administrators. You’ve got this!
Laugh, Learn, and Hoot Up!

Discover and share the latest cybersecurity trends, tips and best practices – alongside new threats to watch out for.

Author: Katie Boquetti | Editorial: Craig Taylor Editorial by Craig Taylor: I remember the early days of...
Read more
Author: Katie Boquetti | Editorial: Craig Taylor Editorial by Craig Taylor: This week's blog has a...
Read more
Every so often a piece of malware comes along with a trick clever enough to make security researchers pause and...
Read moreGet sharper eyes on human risks, with the positive approach that beats traditional phish testing.