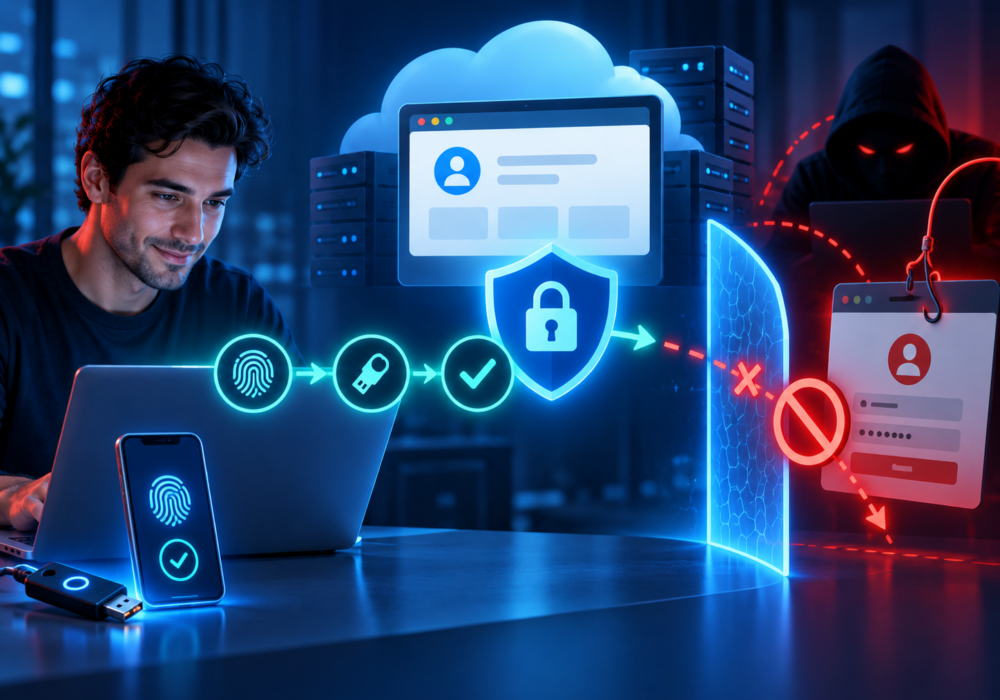
Phishing-resistant multifactor authentication is authentication designed to prevent credentials from being successfully used on an attacker-controlled website.
Traditional MFA methods such as SMS codes, one-time passwords, and simple push notifications provide valuable protection, but sophisticated attackers may still attempt to steal or relay those authentication factors.
Phishing-resistant authentication uses cryptographic techniques that tie the authentication process to the legitimate website or service.
FIDO-based authentication and WebAuthn are widely used examples.
This means that even if a user is tricked into visiting a convincing fake login page, the authentication credential cannot simply be entered into or replayed on the attacker’s site.
SMBs should view phishing-resistant MFA as the long-term direction for securing important business accounts.
Organizations do not necessarily need to migrate every account immediately. A risk-based rollout can begin with:
Passkeys and FIDO security keys can provide phishing-resistant authentication while also reducing dependence on passwords.
MSPs should prioritize phishing-resistant MFA for their own technicians and administrators because compromised MSP credentials may affect many clients.
They can also help customers plan migrations from weaker authentication methods to passkeys, FIDO security keys, and other modern options.
MSPs should consider authentication strength when reviewing client security maturity, cyber insurance requirements, remote access, and privileged-access controls.
Not all MFA provides the same level of protection.
MFA is important, but organizations should move toward authentication that prevents the credential from working on the wrong website in the first place.
Additional Reading:
CyberHoot does have some other resources available for your use. Below are links to all of our resources, feel free to check them out whenever you like:
Discover and share the latest cybersecurity trends, tips and best practices – alongside new threats to watch out for.

Author: Katie Boquetti | Editorial: Craig Taylor Editorial by Craig Taylor: For years we've trained...
Read more
Most phishing tests lie to your employees. This one says hello first! HootPhish tells people up front: this is...
Read more
Severity: CRITICAL (CVSS 9.2) | Issued: October 22, 2026 On October 21, two critical flaws in PHP,...
Read moreGet sharper eyes on human risks, with the positive approach that beats traditional phish testing.