"When we got phished it became pretty clear we needed to do more to protect our company. The same old training just wasn't working. CyberHoot came to the rescue. It's fun, our team loves it, and best of all, it's..."
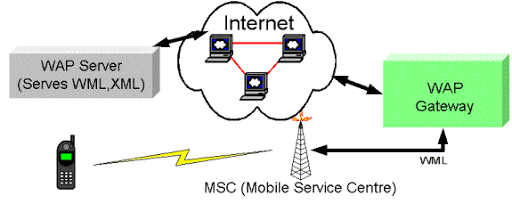
A Wireless Application Protocol (WAP) is an old standard that allowed early mobile phones to access the...
Read more
A Wired Equivalent Privacy (WEP) is a deprecated wireless security protocol that was designed to...
Read more
Linkjacking is a practice used to redirect one website's links to another. Usually, this is...
Read more
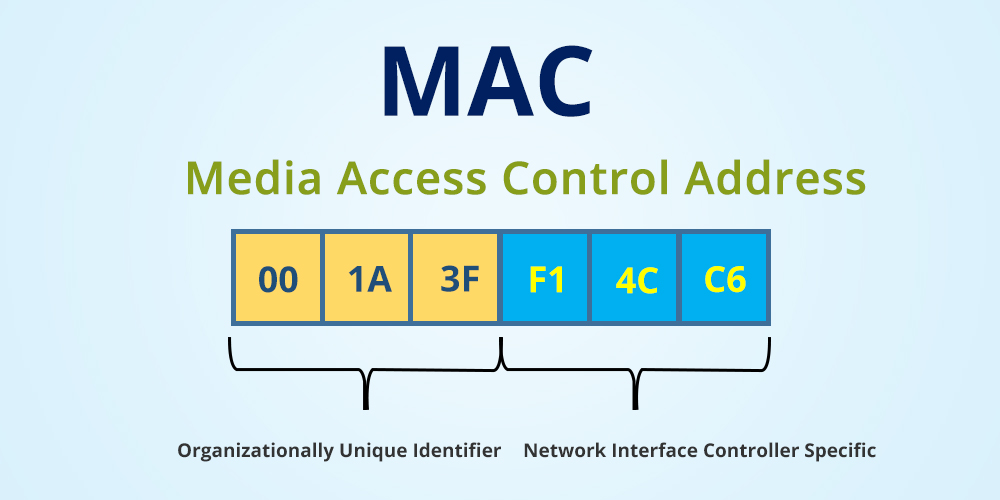
A Media Access Control (MAC) Address is a hardware identification number that is uniquely assigned to...
Read more
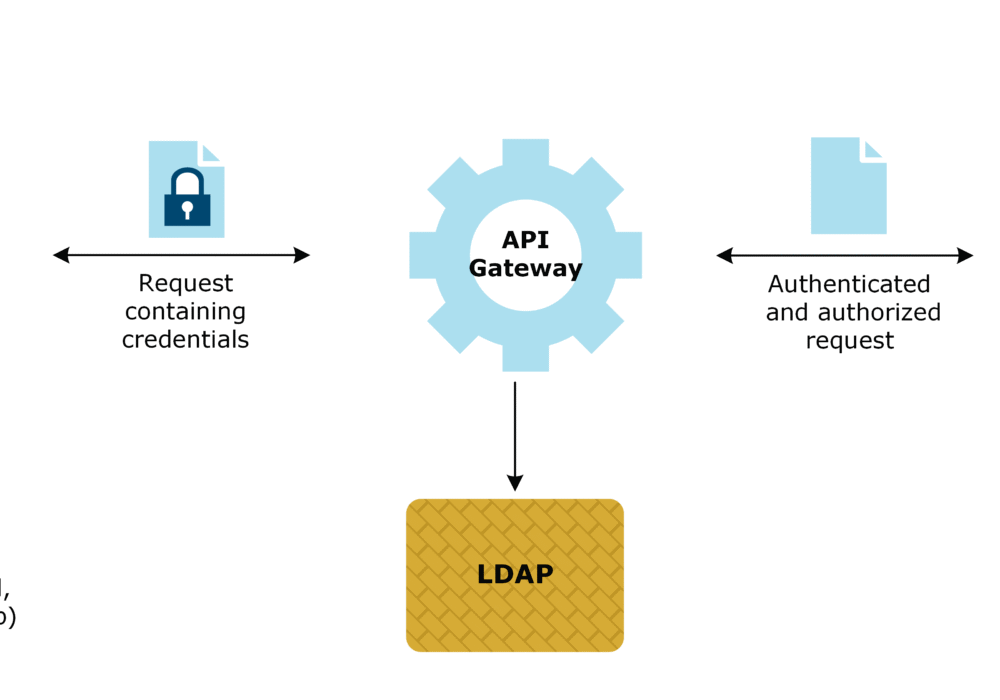
A Lightweight Directory Access Protocol (LDAP) is an open, vendor-neutral, industry standard...
Read more
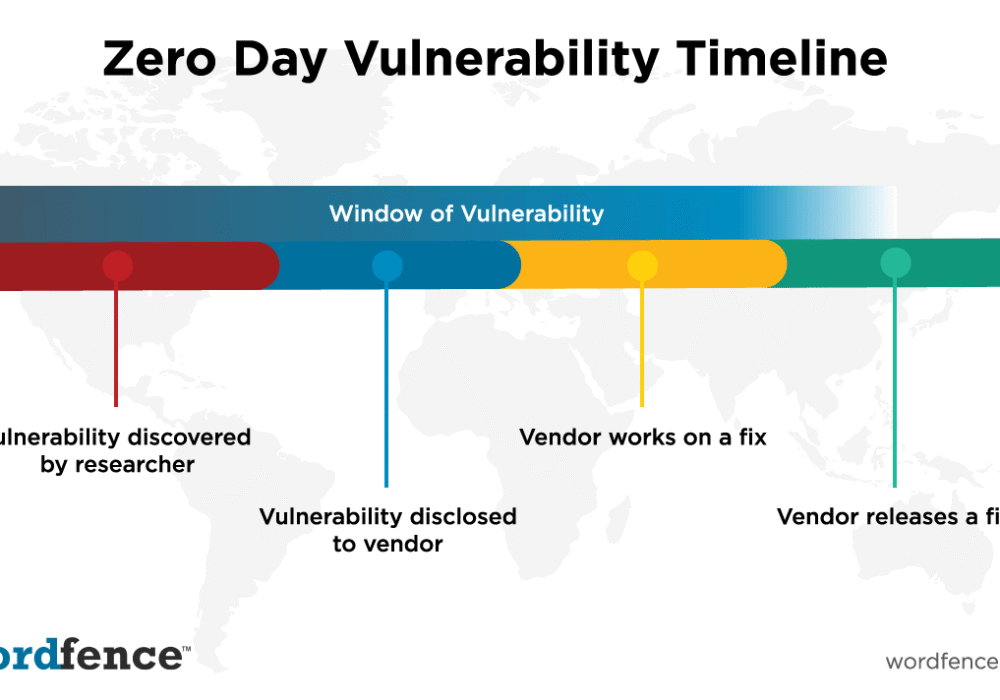
A Zero Day Vulnerability is a security flaw that is unknown to the software vendor or the business it is found...
Read more
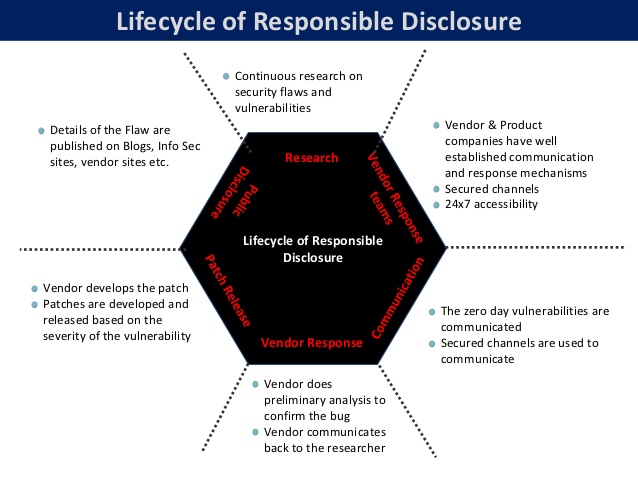
Responsible Disclosure refers to the best practice followed by most security researchers of not...
Read more
Revenge Porn is sexually explicit images or videos of a person posted online without that person's...
Read more
A Privileged User is a user of a computer who is authorized to bypass normal access control mechanisms, usually to...
Read more
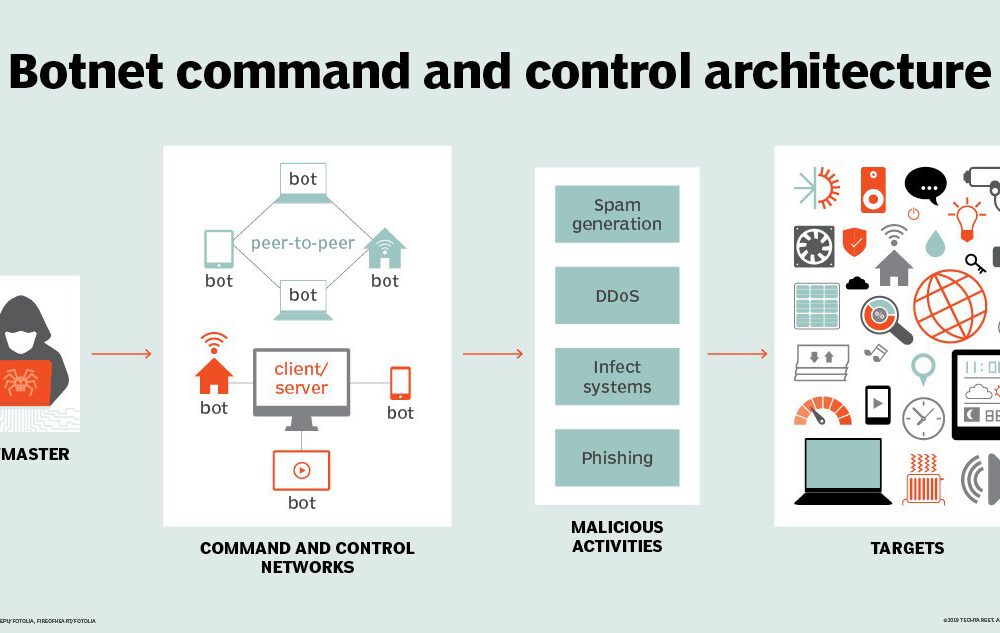
A Command and Control (C&C) Server is a computer being controlled remotely by a cyber criminal that...
Read more
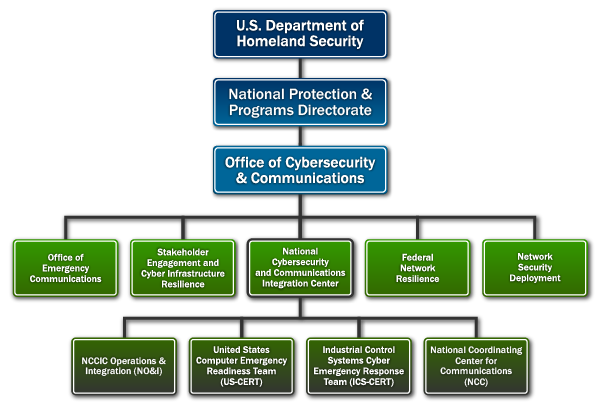
A Computer Emergency Response Team (CERT) is a group of security experts who respond to cybersecurity...
Read moreGet sharper eyes on human risks, with the positive approach that beats traditional phish testing.