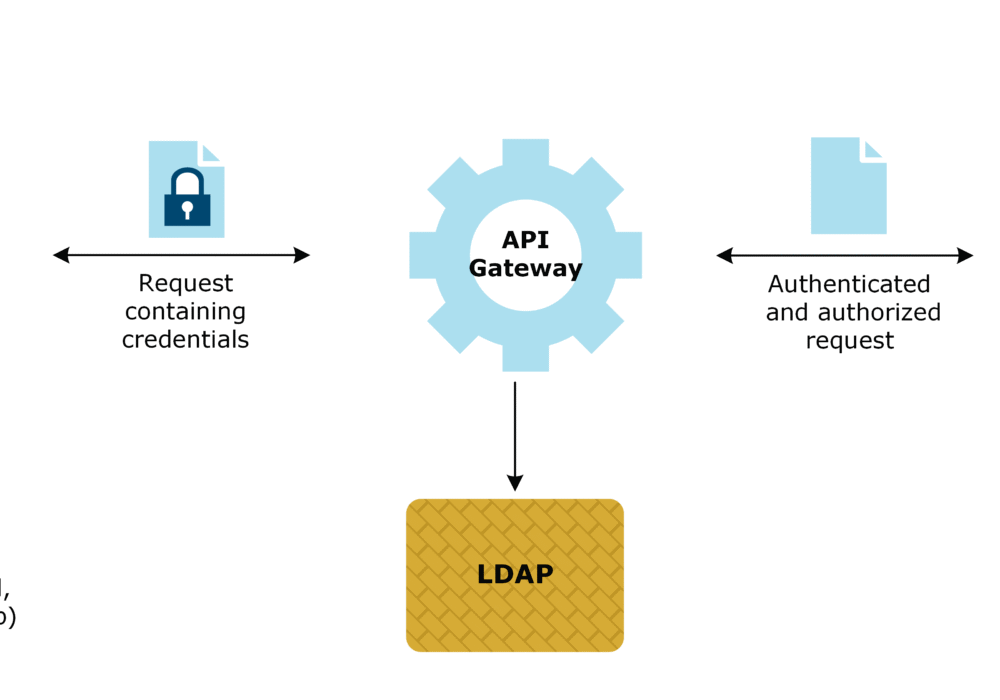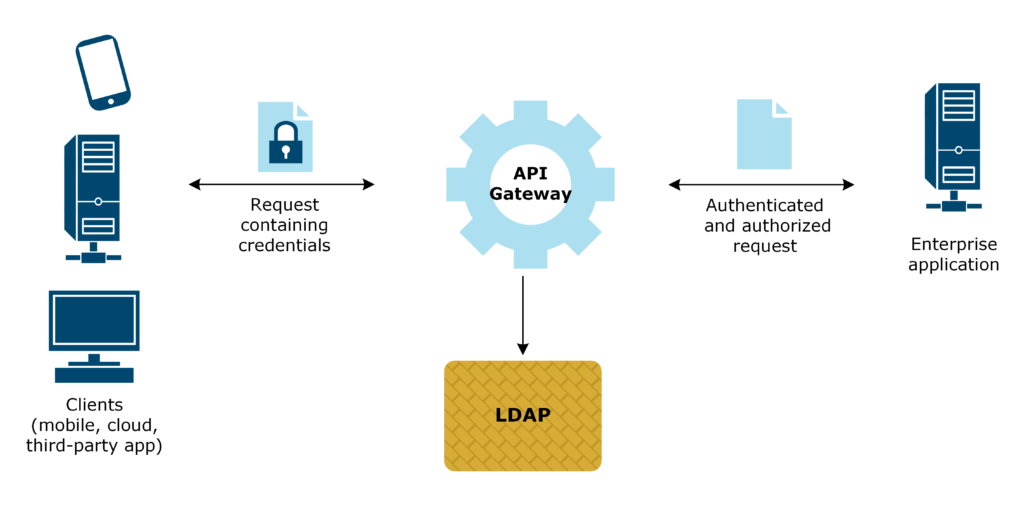
A Lightweight Directory Access Protocol (LDAP) is an open, vendor-neutral, industry standard application protocol for accessing and maintaining distributed directory information services over an Internet Protocol (IP) network. The networks can be on the public internet or on a corporate network. A common use of LDAP is to provide a central place to store usernames and passwords. This allows many different applications and services to connect to the LDAP server to validate users.
Source: TechTarget
Related Terms: Authentication, Two-Factor Authentication
Related Reading: Microsoft Delaying LDAP Configuration Changes to 2H 2020
Definitely. Most businesses need a centralized, authoritative directory of users and their authentication data. Tying LDAP services to your critical applications ensures that you have a single location to manage your users whether auditing, adding, or removing users to those resources. Extremely small companies with fewer than 5 employees may get by without LDAP directory services, but it wouldn’t hurt you to use this either.
Discover and share the latest cybersecurity trends, tips and best practices – alongside new threats to watch out for.

Author: Katie Boquetti | Editorial: Craig Taylor Editorial by Craig Taylor: For years we've trained...
Read more
Most phishing tests lie to your employees. This one says hello first! HootPhish tells people up front: this is...
Read more
Severity: CRITICAL (CVSS 9.2) | Issued: October 22, 2026 On October 21, two critical flaws in PHP,...
Read moreGet sharper eyes on human risks, with the positive approach that beats traditional phish testing.