
Blog > Page 13

Stay sharp with security insights

Quishing

Quishing

Quishing is a type of phishing attack that targets users via QR codes. Attackers create malicious QR codes that,...

Read more
Malvertising

Malvertising

Malvertising is short for malicious advertising. It refers to the use of online ads to deliver malware to...

Read more
Privacy-Enhancing Computation (PEC)

Privacy-Enhancing Computation (PEC)

Privacy-Enhancing Computation (PEC) refers to a set of technologies and methods that allow organizations to...

Read more

Your subscription could not be saved. Please try again.
Almost done! Check your inbox and click the link to confirm your subscription.

Clear Text

Clear Text

Clear Text (or plaintext) is data that is stored or transmitted without any form of encryption or obfuscation. In...

Read more
Privileged Access Management (PAM)

Privileged Access Management (PAM)

Privileged Access Management (PAM) is a cybersecurity framework and set of tools designed to secure, manage, and...

Read more
Identity Management (IDM)

Identity Management (IDM)

Identity Management (IDM) is the framework of policies, processes, and technologies used to ensure the right...

Read more
End-to-End Encryption (E2EE)

End-to-End Encryption (E2EE)

End-to-End Encryption (E2EE) is a method of securing digital communications so that only the sender and the...

Read more
Ad-blockers

Ad-blockers

Ad-blockers are software tools, often installed as browser extensions, apps, or built into browsers, that prevent...

Read more
Operational Disruption

Operational Disruption

Operational Disruption is any unexpected event, failure, or interruption that prevents normal business processes,...

Read more
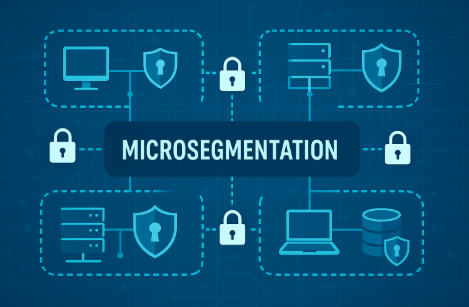
Microsegmentation

Microsegmentation

Microsegmentation is a security technique that divides a network into smaller, isolated zones down to the...

Read more
Why Traditional Phishing Tests Fail — And How the Latest Research Proves It’s Time for a Change

Why Traditional Phishing Tests Fail — And How the Latest Research Proves It’s Time for a Change

For years, organizations have relied on fake email phishing simulations to measure employee resilience to...

Read more
Advisory: CISA Issues Emergency Directive for Critical Microsoft Exchange Flaw

Advisory: CISA Issues Emergency Directive for Critical Microsoft Exchange Flaw

Overview The Cybersecurity and Infrastructure Security Agency (CISA), acting as the U.S. government's cyber...

Read more
Testimonials

See who's talking about CyberHoot

"While it is well known that there are many cyber security threats, sorting out how to protect yourself without accidentally exposing yourself can be a daunting task. For a small organization like ours, this type expertise and time to research..."
Astrid Wielens, Zebra Crossings, Executive Director

"After 9 months of CyberHoot awareness training, a Financial Management firm with $4 Billion in assets was phish tested by the Fellsway Group. They had zero (0%) employees click on the phishing test. In contrast, the exact same phishing attack..."
John Mumford, Fellsway Group, Chief Risk Officer
"CyberHoot has been a game-changer for us - simple to deploy, highly effective in raising awareness, and a great fit for MSPs looking to strengthen client security postures without adding complexity."
Ahmed Albalooshi, Advantari Digital Solutions, CEO
"Easy to implement and get immediate results. Through CyberHoot, I can single-handedly support a company with 500 people in training and policy governance with a minimum of effort. More employees now send me phishing emails they receive, stating 'this is..."
Tim Hurman, Single Digits, System Administrator
"Using CyberHoot was one of the best decisions we made regarding SAT. Fully automated, training is interesting, staff participation is high compared to other vendors."
Max Krider, Creative Tech, HIPAA Compliance Officer