This HowTo article explains how to configure Allow Listing rules in to allow Attack Phishing tests to reach end users using DNS Filter.
Warning: CyberHoot supports fake email Attack-Phishing for customers. Please keep in mind this approach uses negative reinforcement to reduce click rates in employees. To be successful, always pair with Positive Reinforcement, educational, and realistic HootPhish phishing simulations for the best Affect and Effect on end users.
1.) Once you are logged in to DNS Filter, on the right-hand side make sure you are in the company you wish to set up the allow-listing for.
2.) Select Policies > Filtering
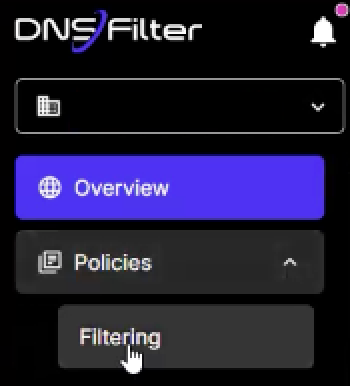
3.) Pick the policy you wish to set up CyberHoot’s Allow-listing or create a new policy
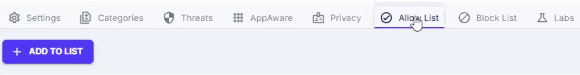
4.) Select the Allow List tab then click + Add To List
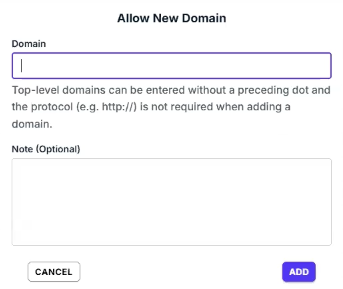
5.) You will see the following pop-up where you can input CyberHoot’s domain names to be allow-listed
For a full list of our DNS Domain names and IP Addresses, follow this link: https://cyberhoot.com/howto/cyberhoots-email-ip-addresses-and-hostnames/
Discover and share the latest cybersecurity trends, tips and best practices – alongside new threats to watch out for.

Author: Katie Boquetti | Editorial: Craig Taylor Editorial by Craig Taylor: For years we've trained...
Read more
Most phishing tests lie to your employees. This one says hello first! HootPhish tells people up front: this is...
Read more
Severity: CRITICAL (CVSS 9.2) | Issued: October 22, 2026 On October 21, two critical flaws in PHP,...
Read moreGet sharper eyes on human risks, with the positive approach that beats traditional phish testing.