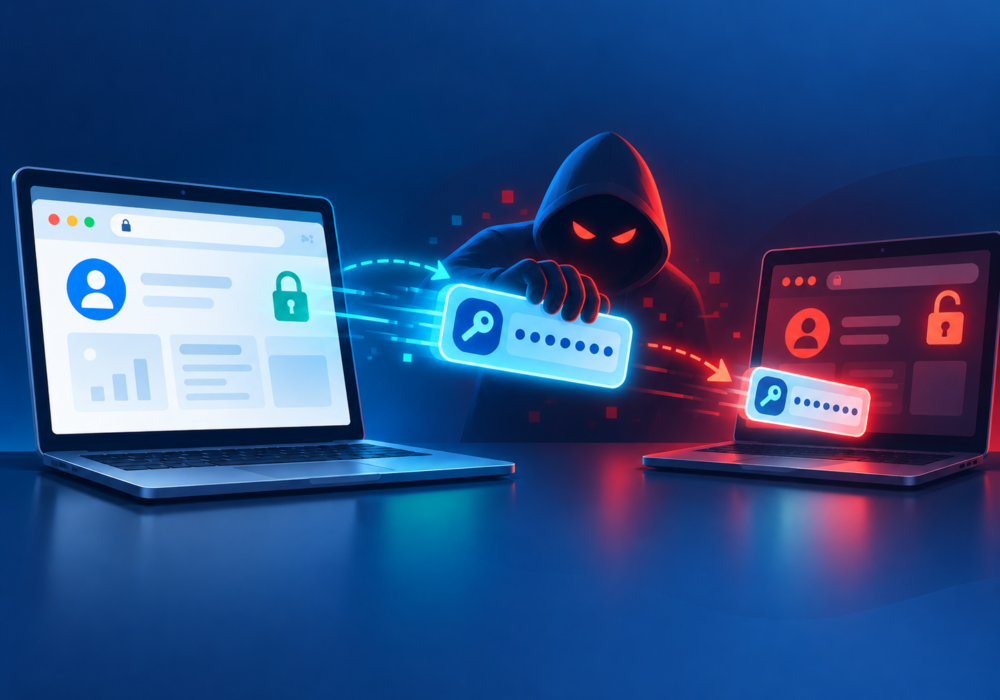
Token theft is the unauthorized stealing of a digital authentication token that represents a user, device, or application’s permission to access a system.
Modern applications frequently use tokens instead of repeatedly transmitting usernames and passwords. Once authentication or authorization is completed, tokens can allow continued access to services or data.
Examples include:
If an attacker steals a valid token, they may be able to impersonate the legitimate user or application.
Microsoft identifies malware and Adversary-in-the-Middle attacks as examples of techniques attackers can use to obtain authentication tokens.
Token theft changes an important assumption about account security: an attacker may not always need your password.
Organizations should protect the devices and applications where authentication tokens are created, stored, and used.
SMBs should:
Employees should also understand that a successful login does not mean an account is permanently safe.
MSPs frequently manage identity providers, cloud platforms, SaaS applications, and administrative accounts for multiple organizations. That makes authentication tokens particularly important to protect.
A compromised privileged token could allow an attacker to access customer systems without going through a normal login process.
MSPs should include token revocation, session review, OAuth application review, and device investigation in account-compromise response procedures.
Monitoring for unusual authentication behavior and anomalous token usage can also help identify potential attacks.
Passwords prove who you are during login. Tokens often prove who you are afterward.
Modern identity security therefore requires organizations to protect both credentials and the tokens created after successful authentication.’s password again. Strong endpoint security, modern authentication, and effective session revocation are all important defenses.
Additional Reading:
CyberHoot does have some other resources available for your use. Below are links to all of our resources, feel free to check them out whenever you like:
Discover and share the latest cybersecurity trends, tips and best practices – alongside new threats to watch out for.

Author: Katie Boquetti | Editorial: Craig Taylor Editorial by Craig Taylor: For years we've trained...
Read more
Most phishing tests lie to your employees. This one says hello first! HootPhish tells people up front: this is...
Read more
Severity: CRITICAL (CVSS 9.2) | Issued: October 22, 2026 On October 21, two critical flaws in PHP,...
Read moreGet sharper eyes on human risks, with the positive approach that beats traditional phish testing.