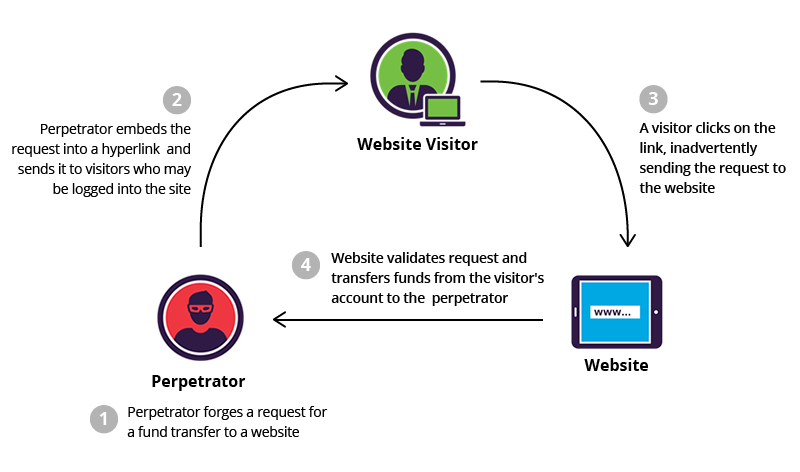
Cross-Site Request Forgery (CSRF), also known as XSRF, is an attack method that fools a web browser into performing unwanted actions in a user application. Similar to Phishing Attacks, CSRFs are typically administered using malicious social engineering, such as an email or link that tricks the victim into sending a forged request to a server. As the unsuspecting user is authenticated by their application at the time of the attack, it’s almost impossible to distinguish a legitimate request from a forged one. A successful CSRF attack can be devastating for both the business and the user. It can result in damaged business relationships, unauthorized money transfers, changed passwords, and data theft. Depending on the nature of the CSRF attack, the hacker may gain full control over the user’s account. If the compromised user has a privileged (administrator) account within the application, the attacker might be able to take full control of all the application’s data and functionality.
Source: Imperva, PortSwigger
Additional Reading: Google and Mozilla Lay Groundwork For A ‘Post-XSS World’
Related Terms: Session Hijacking Attack
Small and medium-sized businesses (SMBs) can perform a number of preventative measures to help prevent and protect your employees against CSRF attacks. From a user’s perspective, prevention is a matter of safeguarding login credentials and denying unauthorized actors access to applications.
Best practices for employees include:
Best practices for companies developing code:
Discover and share the latest cybersecurity trends, tips and best practices – alongside new threats to watch out for.

The takeaway: AI can make familiar cyberattacks faster and easier to scale. Strong security fundamentals still...
Read more
Picture yourself on the highway, cruising about 20 over the limit with the rest of traffic. Up ahead, brake...
Read more
What Is Happening On Thursday, November 12, 2026, around 11 a.m. Eastern, Microsoft Outlook stopped working...
Read moreGive your people sharper eyes, with the positive approach that beats traditional phish testing.

