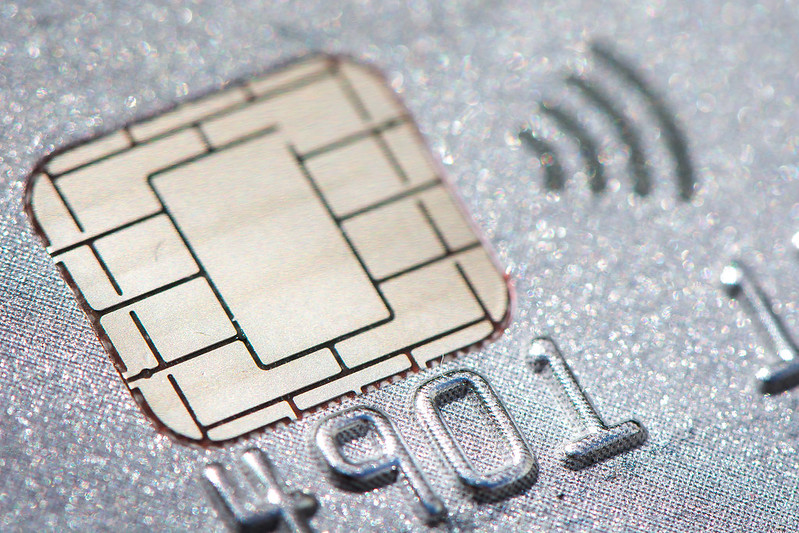
All credit and debit cards are now being made with “a computer that is 1/4 the size of a postage stamp” this technology we know as a chip card. Chip cards are extremely beneficial to the security of cardholder information. When chip cards are inserted, they create a unique transaction ID (also known as Tokenization) every time the card is used; when using the traditional magnetic strip card, you have the same transaction ID every time making you vulnerable to hackers.
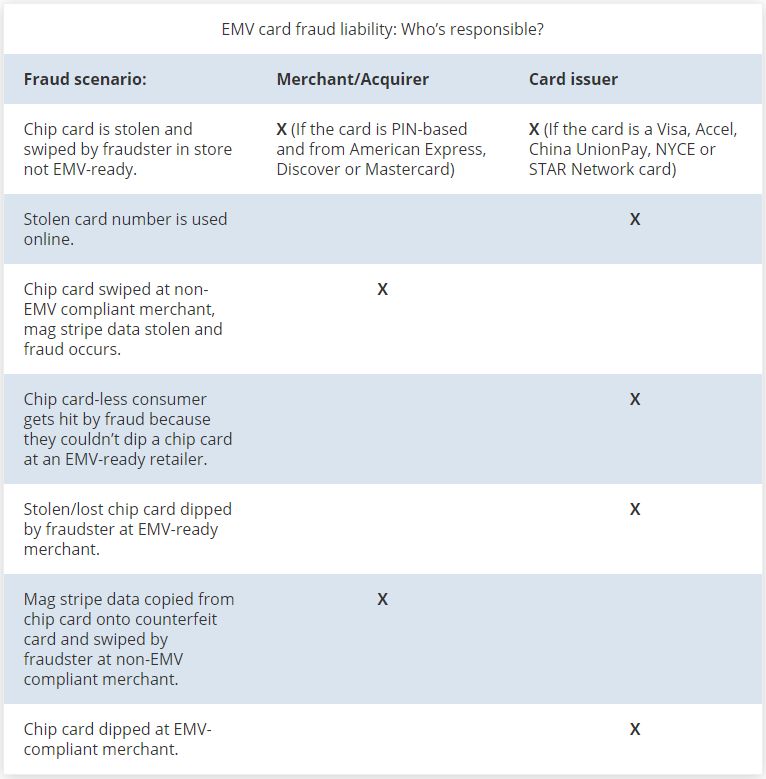
For companies processing Credit Cards transactions, the liability shifted after Oct. 1st 2015. The graphic below outlines who is responsible for fraudulent transactions based upon how the fraud occurs and the level of protection and use of Chip technology at the company accepting the Credit Card for processing.
Discover and share the latest cybersecurity trends, tips and best practices – alongside new threats to watch out for.

Author: Katie Boquetti | Editorial: Craig Taylor Editorial by Craig Taylor: For years we've trained...
Read more
Most phishing tests lie to your employees. This one says hello first! HootPhish tells people up front: this is...
Read more
Severity: CRITICAL (CVSS 9.2) | Issued: October 22, 2026 On October 21, two critical flaws in PHP,...
Read moreGet sharper eyes on human risks, with the positive approach that beats traditional phish testing.