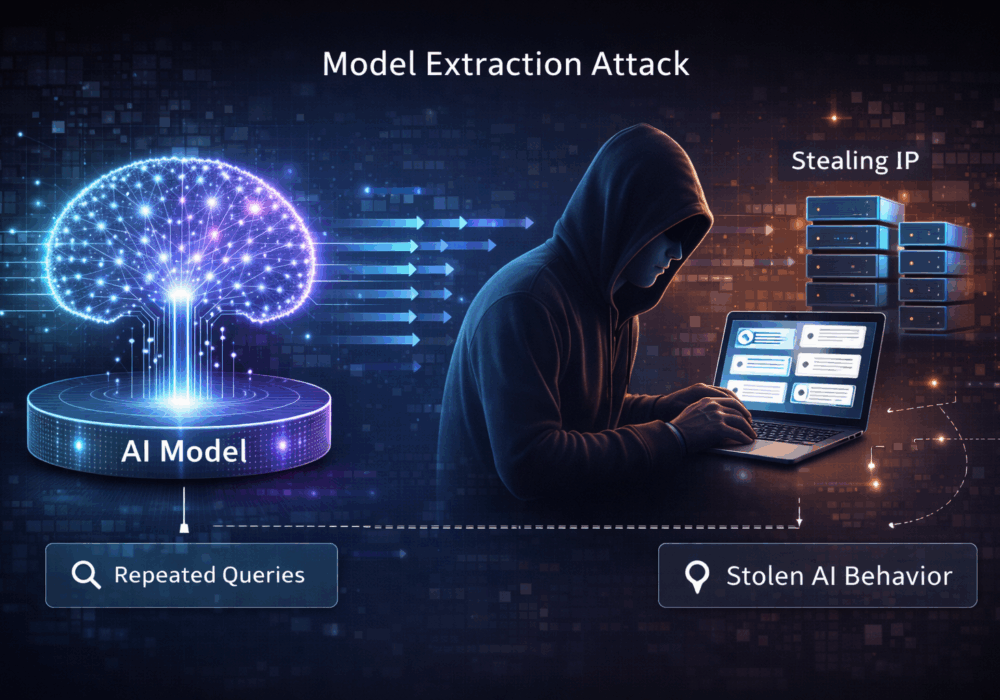
A model extraction attack is a technique in which an adversary repeatedly queries a hosted machine learning or AI model to infer, replicate, or approximate its internal behavior. Over time, the attacker can build a surrogate model that closely mimics the original, effectively stealing intellectual property without direct access to the model’s code or weights.
These attacks exploit:
The goal is not data theft, but model theft.
For small and medium-sized businesses, model extraction is often an invisible risk, especially when offering AI-powered features externally.
Key implications include:
For SMBs, model extraction turns AI from an asset into a liability if protections are not in place.
For Managed Service Providers, the stakes are higher and broader.
Key considerations include:
Model extraction attacks target how a model behaves, not how it is built.
For SMBs and MSPs:
Additional Reading:
CyberHoot does have some other resources available for your use. Below are links to all of our resources, feel free to check them out whenever you like:
Discover and share the latest cybersecurity trends, tips and best practices – alongside new threats to watch out for.

Most phishing tests lie to your employees. This one says hello first! HootPhish tells people up front: this is...
Read more
Severity: CRITICAL (CVSS 9.2) | Issued: October 22, 2026 On October 21, two critical flaws in PHP,...
Read more
Author: Katie Boquetti | Editorial: Craig Taylor Editorial by Craig Taylor: Even before Claude Code made...
Read moreGet sharper eyes on human risks, with the positive approach that beats traditional phish testing.