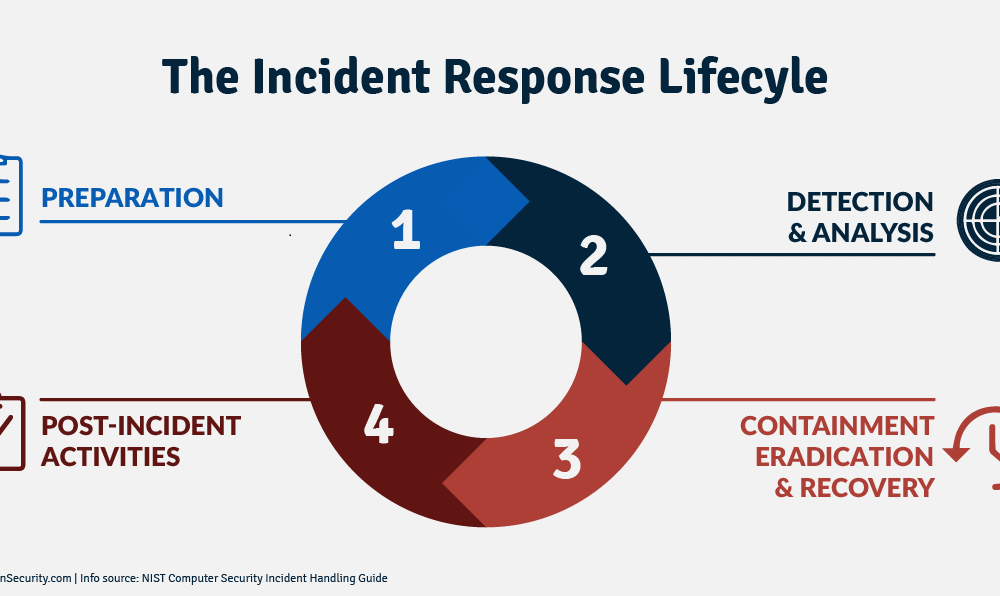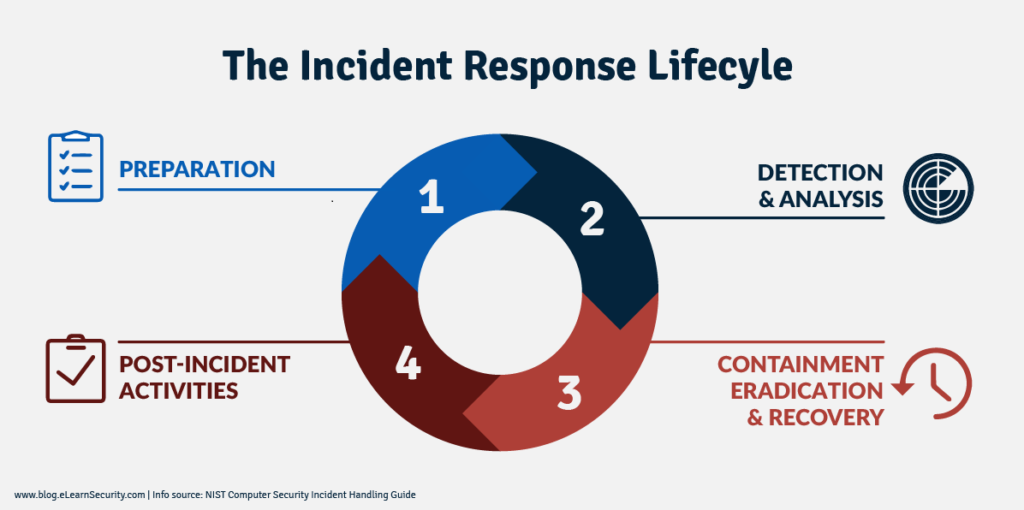
Eradication refers to what happens following containment of a cyber attack incident. After the threat has been contained, it is necessary to eradicate (remove) key components of the security incident. Removing malware from all infected systems that were moved offline during the containment phase would be done in the eradication phase of an incident. Common examples of eradication tasks include disabling and resetting breached user accounts, resetting passwords on all domain accounts, and scanning the network for indicators of compromise. Eradication is key to prevent attackers from launching additional attacks on your company.
If you own a business, you need to be doing these basic things to protect your sensitive information:
Most of these recommendations are built into CyberHoot. With CyberHoot you can govern, train, assess, and test your employees. Visit CyberHoot.com and sign up for our services today. At the very least continue to learn by enrolling in our monthly Cybersecurity newsletters to stay on top of current cybersecurity updates.
Related Term: Containment, Recovery, Revision, Root Cause Analysis
Source: Bluegrass Cyber Security
Discover and share the latest cybersecurity trends, tips and best practices – alongside new threats to watch out for.

Picture yourself on the highway, cruising about 20 over the limit with the rest of traffic. Up ahead, brake...
Read more
What Is Happening On Thursday, November 12, 2026, around 11 a.m. Eastern, Microsoft Outlook stopped working...
Read more
Author: Katie Boquetti | Editorial: Craig Taylor Editorial by Craig Taylor: “Power tends to corrupt,...
Read moreGet sharper eyes on human risks, with the positive approach that beats traditional phish testing.