When Phish testing environments where Sophos EDR is present, you will need to enable allow listing and add the CyberHoot addresses. Otherwise the Website Management defenses will intercept any attempt to click on a link taking you to a nefarious phish testing website.
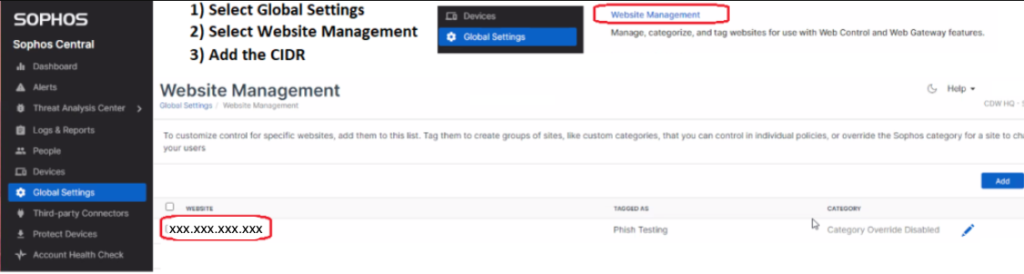
There are three steps to accomplish this as shown in the graphic above.
Discover and share the latest cybersecurity trends, tips and best practices – alongside new threats to watch out for.

Most phishing tests lie to your employees. This one says hello first! HootPhish tells people up front: this is...
Read more
Severity: CRITICAL (CVSS 9.2) | Issued: October 22, 2026 On October 21, two critical flaws in PHP,...
Read more
Author: Katie Boquetti | Editorial: Craig Taylor Editorial by Craig Taylor: Even before Claude Code made...
Read moreGet sharper eyes on human risks, with the positive approach that beats traditional phish testing.