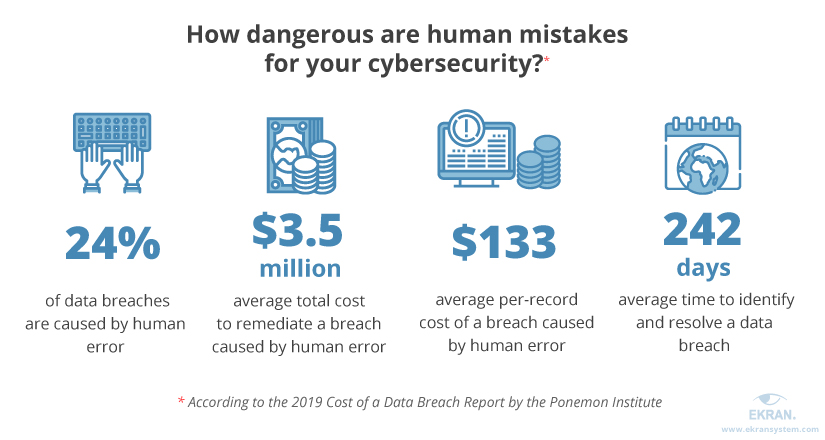
An Accidental Insider Threat occurs when an employees’ actions lead to damage to a system or network, the loss of critical or sensitive data, or even where a helpful employee holds a door open for a hacker to enter a secure building. These incidents can occur with zero malicious intent, making the incidents accidental in nature, but they still can be very damaging to the company in question.
Examples include: an employee accidentally deletes an important document; an employee falls victim to a spear-phishing attack introducing ransomware into a company’s network; and when an employee accidentally shares more information with a client or 3rd party than they are legally allowed to.
Related Terms: Data Loss Prevention, Insider, Malicious Insider Threat
Educate your employees that cybersecurity incidents by hackers outside the company often cannot be successful without an internal employee making a mistake. Internal threats exist that are both accidental and malicious in nature. Educating your staff to be vigilant in watching for inside threats or mistakes, is a critical piece of your SMB’s cybersecurity awareness program.
All threats against your company, whether a disgruntled employee, or simply an employee who isn’t properly trained can lead to very damaging consequences. Here are a few prevention tips to reduce the risk of this happening:
There are other steps one can take, but the four above represent a good starting place for SMB owners to building a strong cybersecurity program. With awareness comes better security.
Discover and share the latest cybersecurity trends, tips and best practices – alongside new threats to watch out for.

Picture yourself on the highway, cruising about 20 over the limit with the rest of traffic. Up ahead, brake...
Read more
What Is Happening On Thursday, November 12, 2026, around 11 a.m. Eastern, Microsoft Outlook stopped working...
Read more
Author: Katie Boquetti | Editorial: Craig Taylor Editorial by Craig Taylor: “Power tends to corrupt,...
Read moreGive your people sharper eyes, with the positive approach that beats traditional phish testing.

